Leaderboard
-
bluedevil
Full Member4Points61Posts -
lovejoy226
Full Member+4Points1,467Posts -
whoknows
Full Member+4Points2,060Posts -
Visual Studio
Junior+3Points15Posts
Popular Content
Showing content with the highest reputation since 11/01/2025 in Files
-
 5 pointsA collection of tutorials aimed particularly for newbie reverse engineers. 01. Olly + assembler + patching a basic reverseme 02. Keyfiling the reverseme + assembler 03. Basic nag removal + header problems 04. Basic + aesthetic patching 05. Comparing on changes in cond jumps, animate over/in, breakpoints 06. "The plain stupid patching method", searching for textstrings 07. Intermediate level patching, Kanal in PEiD 08. Debugging with W32Dasm, RVA, VA and offset, using LordPE as a hexeditor 09. Explaining the Visual Basic concept, introduction to SmartCheck and configuration 10. Continued reversing techniques in VB, use of decompilers and a basic anti-anti-trick 11. Intermediate patching using Olly's "pane window" 12. Guiding a program by multiple patching. 13. The use of API's in software, avoiding doublechecking tricks 14. More difficult schemes and an introduction to inline patching 15. How to study behaviour in the code, continued inlining using a pointer 16. Reversing using resources 17. Insights and practice in basic (self)keygenning 18. Diversion code, encryption/decryption, selfmodifying code and polymorphism 19. Debugger detected and anti-anti-techniques 20. Packers and protectors : an introduction 21. Imports rebuilding 22. API Redirection 23. Stolen bytes 24. Patching at runtime using loaders from lena151 original 25. Continued patching at runtime & unpacking armadillo standard protection 26. Machine specific loaders, unpacking & debugging armadillo 27. tElock + advanced patching 28. Bypassing & killing server checks 29. Killing & inlining a more difficult server check 30. SFX, Run Trace & more advanced string searching 31. Delphi in Olly & DeDe 32. Author tricks, HIEW & approaches in inline patching 33. The FPU, integrity checks & loader versus patcher 34. Reversing techniques in packed software & a S&R loader for ASProtect 35. Inlining inside polymorphic code 36. Keygenning 37. In-depth unpacking & anti-anti-debugging a combination packer / protector 38. Unpacking continued & debugger detection by DLL's and TLS 39. Inlining a blowfish scheme in a packed & CRC protected dll + unpacking Asprotect SKE 2.2 40. Obfuscation and algorithm hiding5 points
-
3 pointsI want to release a new tutorial about the popular theme Themida - WinLicense. So I see there seems to be still some open questions mostly if my older unpack script does not work anymore and the unpacked files to, etc. So this time I decided to create a little video series on how to unpack and deal with a newer protected Themida target manually where my older public script does fail. A friend of mine did protect unpackme's for this and in the tutorial you will see all steps from A-Z to get this unpackme successfully manually unpacked but this is only one example how you can do it, of course. So the tutorial [videos + text tutorial] is very long and has a run-time of more than three hours and of course it will be necessary that you also read the text parts I made at the same time if possible but if you are already a advanced user then you will have it easier than a newbie. So I hope that you have enough patience to work through the whole tutorial. So the main attention I set on all things which happen after normal unpacking so the unpack process is the simplest part and all what comes after is the most interesting part and how to deal with all problems that happen. It's more or less like a live unpack session. I also wrote some small basic little helper scripts which you can also use for other targets to get valuable information if you need. Short summation: Unpacking Exception analysing VM analysing with UV plugin AntiDump's find & fixing & redirecting "after fix method" Testing on other OS My Special Thanks goes to Lostin who made this unpackme and others + OS's tests. (I want to send a thank you to Deathway again for creating this very handy and helpfully UV plugin). So this is all I have to say about the tutorial so far, just watch and read and then try it by yourself. Oh! and by the way I record ten videos and not only one. If something does not work or you have any problems with this tutorial, etc. then ask in the support topic only. Don't send me tons of PM's, OK! Thank you in advance. PS: Oh! and before someone has again something to complain because of my tutorial style [goes to quickly or is bad or whatever] then I just want to say, maybe you're right so normally I don't like to create and write tutorials. This is really not my thing so keep this in your mind.3 points
-
 2 pointshey guys i create a program for serial sniff by vb6 esc features : check crc(automatic) unicode string small size background music bypass packers and ..... sorry for my english (im persian) enjoy it2 points
-
2 pointsThis is a complete archive (site rip) of all files on Tuts 4 You as of July 2011 except for the malware samples - you will need to download these directly from Tuts 4 You. I have created the torrent as directories and files rather than one archive which gives you the option to download files individually or in categories. The entire collection is 3.69 GB of which some sections may be of little interest to some but you have the option of downloading what you want. This collection will be updated annually so please check at the following link for the official and up-to-date torrent file. Base 32 Hash-ID magnet:?xt=urn:btih:slpgvubkpp4dyhxbaxpmogludkgmw7wi Base 16 Hash-ID magnet:?xt=urn:btih:92DE6AD02A7BF83C1EE105DEC719741A8CCB7EC8 Please remember to seed the torrent and help share the knowledge within the reversing community. I hope this satisfies the leechers, thank you! File/ Directory Listing Tuts 4 You - Collection 2011.md52 points
-
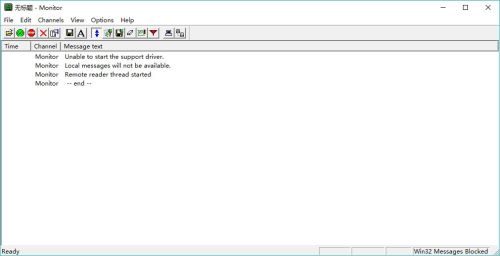 DriverMonitor Enhanced Edition (Alpha) Enhance - 1 - Support for file dragging operations has been implemented, allowing direct setting of the path for the corresponding driver file. - 2 - Drag-and-drop operation compatible with administrator mode has been implemented. - 3 - Folder directory redirection in 64-bit environment has been disabled. Modified by boot @ tuts4you Date July 6, 20262 points
-
2 points
 IDA Palette (or its project name: ifred) is a plugin which provides fast search on IDA Pro's commands/menu items or searches through its strings output! This plugin provides 2 keyboard shortcuts: Ctrl + P : Searched through IDA's commands Ctrl + Shift +P : Searched through IDA's string output2 points
-
2 points
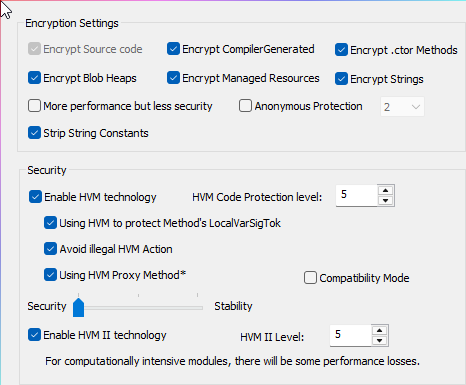 So this is my first upload - I hope I am doing this right. I have included all the protections in the screenshots being used. Good luck2 points
-
The Hex-Rays Decompiler plugin for better code navigation in RE process. CodeXplorer automates code REconstruction of C++ applications or modern malware like Stuxnet, Flame, Equation, Animal Farm ... Features: Automatic type REconstruction for C++ objects. To be able to reconstruct a type using HexRaysCodeXplorer one needs to select the variable holding pointer to the instance of position independed code or to an object and by right-button mouse click select from the context menu «REconstruct Type» option. Virtual function table identification - automatically identifies references to virtual function tables during type reconstruction. When a reference to a virtual function table is identified the plugin generates a corresponding C-structure. As shown below during reconstructing struct_local_data_storage two virtual function tables were identified and, as a result, two corresponding structures were generated: struct_local_data_storage_VTABLE_0 and struct_local_data_storage_VTABLE_4. C-tree graph visualization – a special tree-like structure representing a decompiled routine in citem_t terms (hexrays.hpp). Useful feature for understanding how the decompiler works. The highlighted graph node corresponds to the current cursor position in the HexRays Pseudocode window Ctree Item View – show ctree representation for highlighted element Extract Types to File – dump all types information (include reconstructed types) into file. Navigation through virtual function calls in HexRays Pseudocode window. After representing C++ objects by C-structures this feature make possible navigation by mouse clicking to the virtual function calls as structure fields Jump to Disasm - small feature for navigate to assembly code into "IDA View window" from current Pseudocode line position. It is help to find a place in assembly code associated with decompiled line. Object Explorer – useful interface for navigation through virtual tables (VTBL) structures. Object Explorer outputs VTBL information into IDA custom view window. The output window is shown by choosing «Object Explorer» option in right-button mouse click context menu Support auto parsing RTTI objects This plugin is recompiled by disauto UPDATE 29.10.2024 Recompiled for IDA Pro v9.0 Windows x86_642 points
-
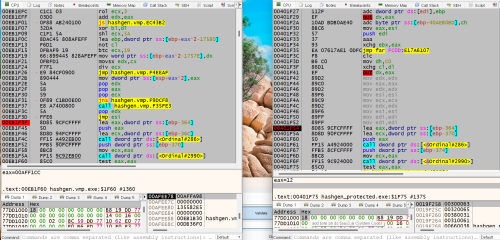 I want you guys who are capable of unvirtualizing and unpacking them to upload the final ones. These files are just the same part of the codes virtualized which are 2 lines of the original mfc source codes. So if you can unvirtualize them and unpack them, please upload the final ones. Any other protections are excluded absolutely. Give it a try and improve your skills. Best Regards. sean.2 points
-
2 pointsThe idea for this project was to provide a means of publication for interesting articles. Not everyone likes to write tutorials, and not everyone feels that the information they have is enough to constitute a publication of any sort.We all run across interesting protections, new methods of debugger detection, and inventive coding techniques.We just wanted to provide the community with somewhere to distribute interesting, sometimes random, reversing information. While the title of this ezine says ARTeam, we prefer to think that we are acting as a conduit. We really hope that you find this project interesting, and we really want this to be a community project. So if you have an idea for an article, or just something fascinating you want to share, let us know and hopefully we will see a ezine #. It soon became apparent that the scope of this project went well beyond what we had predicted. A big thanks goes out to all the contributors. Without you this would be a blank page. We also need to thank everyone who has viewed, refined and commented on the production of this ezine. Hopefully we have been able to provide the reversing community something interesting. The reversing community has been very dynamic in the past few years. We've seen a ring GUI debugger grow in startling popularity. We've seen protection authors dig deeper into the OS in an effort to deter crackers. Unique protections have provided months of analysis for reversers. New inventive tools have been developed in the re-versing community in an effort to effectively analyze and understand software protection. And ironically we see some of these tools move back to ring0. None of these changes and achievements would have been possible without the amazing and talented reversers that take the time to share their knowledge and teach others. No matter what team you belong to, what level you reverse at, what language you speak, you all make up the same community. A group of people who constantly strive for discovery. None of us are content with accepting things "as they are" we need to know why. We are the scientists of software. We dig deeper than the average user, we see code where everyone else see flashy presentation. We learn this code so well that we can rewrite it, manipulate it, and even improve on it. Since these are my thoughts, I just want to thank every single member of the reversing community. I couldn't even begin to name every single person who has provided a contribution. We are all spread out among many boards, many teams, even many countries. But I like to think that we all share a certain camaraderie. Please enjoy the information included among these pages, we had some talented people give us some great sub-missions.2 points
-

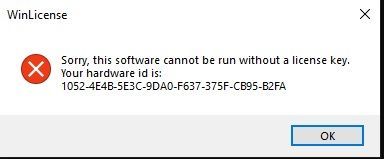 WinLicense 3.2.3 CrackMe. The goal is to bypass WinLicense. No antidebug or virtualization is used. The file is just packed with WinLicense. Silver medal if you manage to bypass. Gold if you unpack the file. If you find it easy can make it some levels harder but i think it is enough hard for the most users or the forum.1 point
-
 1 point
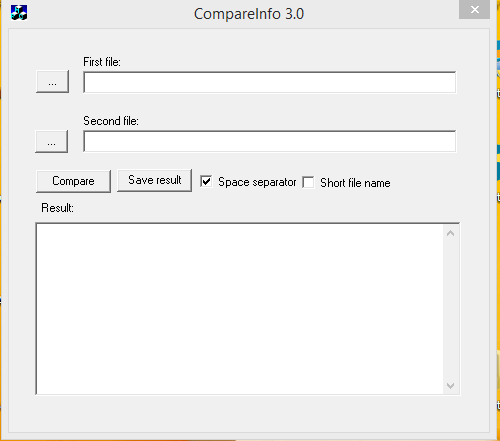
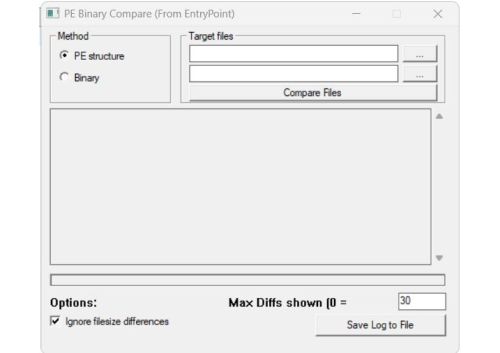 What does the tool do? The program is a graphical Windows application (Win32 GUI) for the byte-accurate comparison of two executable files (e.g. B. .exe or .dll). The special feature of this is that the binary comparison does not start at the beginning of the file, but at the respective entry point (entry point) of the program code. This allows modifications or patches to be detected in the executable code, even if the file sizes or header metadata differ fundamentally from each other. Core functions & features ⚙️ Intelligent PE header analysis: The tool automatically detects whether it is a 32-bit (PE32) or 64-bit (PE32+) Windows file. It reads the virtual address of the Entry Point (AddressOfEntryPoint) and translates it to the real file offset on the hard drive. 🔍 Synchronized byte comparison: After the offset calculation, the tool jumps exactly to the code start point in both files and compares bytes for byte (via a high-performance file loop) from there. 📏 Ignore size differences: Enable the option “Ignore filesize differences”, the tool compares the data until the shorter of the two files reaches its end. A difference in size therefore does not lead to a premature termination. 📝 Detailed error log (log): Deviations found are output directly in the UI. The tool shows the relative offset (from the entry point) and the absolute offset for both files separately, including the different hex values (e.g. B. 0x90 ! = 0xCC). To keep the log readable, the maximum of the first 30 Differences listed.1 point
-
 1 point
-

 Anti Debug Anti Tamper Delegate Proxy Resource Protect String Virtualization ControlFlow And Mutation Code Virtualization Renamer1 point
-
 1 point
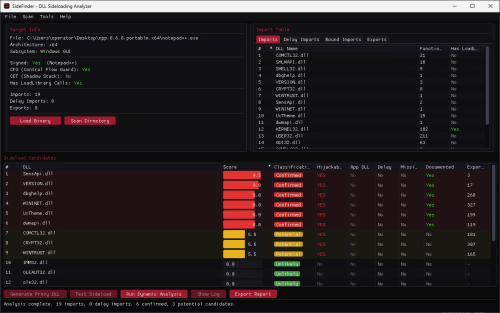 A Windows tool for identifying and analyzing potential DLL sideloading opportunities in Portable Executable files. SideFinder is a Windows GUI application designed to streamline the discovery and analysis of DLL sideloading opportunities in Portable Executable files. It combines static PE inspection, candidate classification, dynamic monitoring, and supporting workflows in a single interface for security research and authorized testing. Features: Parses x86 and x64 PE files, including regular, delayed, bound imports, and exported functions. Identifies and ranks potential DLL sideloading candidates using contextual scoring and classification. Reviews relevant binary properties such as Authenticode signatures, CFG, CET, subsystem, architecture, and LoadLibrary usage. Resolves DLL search paths, KnownDLLs, missing libraries, and DLLs already present alongside the target application. Runs dynamic analysis to observe DLL loads and cross-reference runtime behavior with static findings. Scans complete directories and summarizes candidates across multiple executables and libraries. Optionally enriches results with the community-maintained HijackLibs dataset. Generates ready-to-use proxy or sideload DLLs with customizable payload options, including MessageBox, Shellcode Runner, and custom-code presets. Provides one-click sideload testing with a harmless MessageBox payload to confirm whether a candidate works. Exports analysis results and keeps an activity log for later review. Read the full article at redteamer.es and explore the project on SideFinder.1 point
-
1 point
 Goal : Find valid username & serial Compiler : C++ Platform : x64-Windows Packed : No Specification : Internal private obfuscation Rule : don't patch binary Note : there is no asymmetric encryption , so you can find it.1 point
-
 1 point
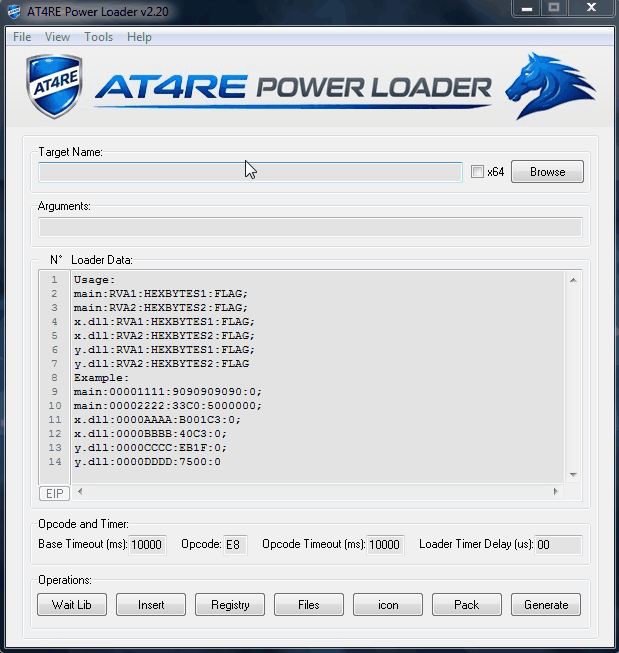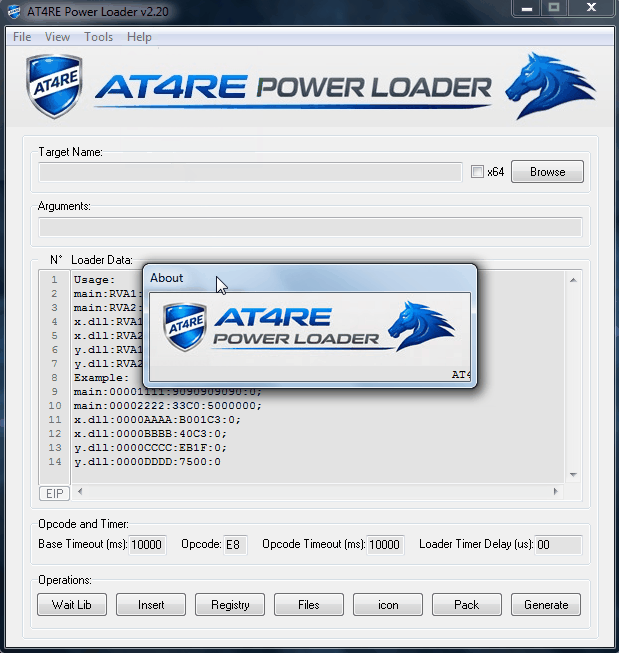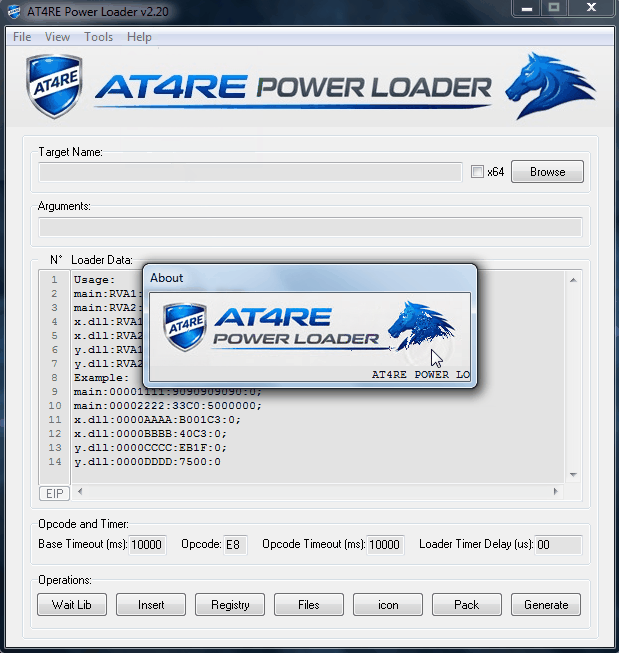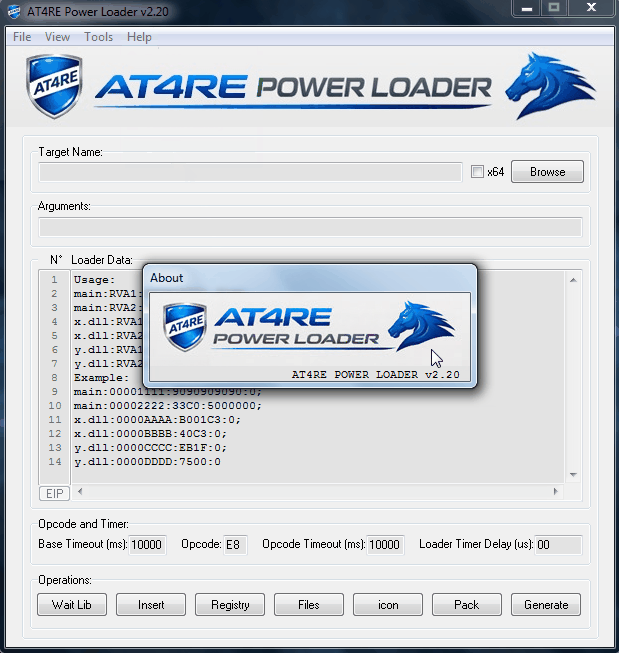 ============================ AT4RE Power Loader v0.1 (Release Date: 26/03/2025) ============================ [+] Console interface [+] Loader Coded in C++ with CRT (big Size: 85 KB when compressed about 190 KB uncompressed). [+] Supports patching single or multiple Relative Virtual Addresses (RVAs). Root Folder Contents: [+] ATPL.EXE (AT4RE Power Loader) [+] Version History.txt ============================ AT4RE Power Loader v0.2 (Release Date: 16/04/2025) ============================ The most powerful loader against strong and hard protectors. It also works with medium-level protectors, packers, compressors, and even unprotected executable files. Main Features: [+] GUI Coded in Borland Delphi 7 [+] From the GUI, you can browse to select the target file (maximum filename length is 255 characters). [+] You can also copy and paste the file name into the input field. [+] Choose between x32 and x64 loader versions. [+] Loader data can be entered only in the format shown in filed or in the screenshot. [+] Set a base timeout in milliseconds (Minimum: 00, Maximum: 9999 — i.e., 9.99 seconds). [+] Set 1-byte opcodes in the Opcode field using HEX characters (Opcode is the Original First Byte of RVA1). [+] Configure Opcode Timeout in milliseconds (Minimum: 00, Maximum: 9999 — i.e., 9.99 seconds). [+] Set the Loader Timer Delay in microseconds (Min: 00, Max: 9,999,999 — i.e., 9.99 seconds). [+] Configure the loader to start as Administrator. [+] Directly pack the loader with UPX. [+] Generate Loader.exe [+] Save or open projects for future use from File menu. [+] Set the GUI to "most on top" from the View menu. [+] Access the official website, report bugs, and find more information via about in the Help menu. Loader Details: [+] Coded in C++ using the Windows Pure API. [+] Loader size is 10 KB uncompressed, and 5 KB when compressed. [+] Supports Windows 7, 8, 10, and 11 (both x32 and x64). Features include: [+] Anti-ASLR [+] Anti-Anti-Debug [+] Anti-CRC Check [+] Automatically detects the base address. [+] Detects when the protector unpacks code into memory. [+] Can apply temporary patches after a specified delay in microseconds (Patch and restor original bytes). [+] Can apply permanent patches only with 00 Flag [+] Supports patching single or multiple Relative Virtual Addresses (RVAs). [+] Capable of patching up to 2048 bytes. [+] Can run as Administrator or Normal user mode. Root Folder Contents: [+] Project folder (Save or open projects for future use) [+] UPX folder (includes upx32.exe and upx64.exe) [+] ATPL.EXE (AT4RE Power Loader) [+] Version History.txt ============================ AT4RE Power Loader v0.3 (Release Date: 10/05/2025) ============================ The most powerful loader against strong and hard protectors. It also works with medium-level protectors, packers, compressors, and even unprotected executable files. Main Features: [+] Added Support Patching DLLs (Only DLLs Loaded by Target.exe). [+] Added Drag Drop Feature: For .EXE, .REG, .ICO Files. [+] Added Insert Loader Data feature (For Respect the Correct Format). [+] Added Registry Keys Manager (Max size: 1 KB / 1024 characters). [+] Added Delete Files feature (Max size: 1 KB / 1024 characters). [+] Added Icon Changer. [+] Added New Project option from File menu (Clears all fields). [+] Added Commands Shortcut Ctrl+N, Ctrl+O, Ctrl+S in File menu. [+] Added Contact Us section from Help menu. [+] Updated About from Help menu from box to a form. [+] Updated display fonts for Loader Data, Registry, and Files. [-] Removed "My Target run as admin". Loader Details: [+] Size is now 17 KB uncompressed, 7 KB when compressed. [+] Loader now Support Patching DLLs (Only DLLs Loaded by Target.exe). [+] Loader can now add or delete registry keys. [+] Loader can delete files. [+] Automatically requests Run as Administrator when needed (e.g.,Target need administrator privilege, modifying registry or deleting files from protected folders). [+] Icon support added. Root Folder Contents: [+] Icons folder (includes 5 icons). [+] Lib folder (includes bass.dll). [+] Project folder (Save or open projects for future use). [+] ResH folder (includes ResHacker.exe). [+] UPX folder (includes upx32.exe and upx64.exe). [+] ATPL.EXE (AT4RE Power Loader). [+] Version History.txt ============================ AT4RE Power Loader v0.4 (Release Date: 16/05/2025) ============================ The most powerful loader against strong and hard protectors. It also works with medium-level protectors, packers, compressors, and even unprotected executable files. Main Features: [+] Added Import menu. [+] Added Support .1337 patch files exported by x64dbg. [+] Set Opcode automatically when Load .1337 file. [+] Added OpenDialog when Double Click on: - Target Name field. - Loader Data field. - Registry field. - Custom icon field. Loader Details: [+] Fixed bug with registry feature. [+] Default icon changed. [+] Compressed Loader with Default icon 8 KB. Root Folder Contents: [+] Icons folder (includes 5 icons). [+] Lib folder (includes bass.dll). [+] Project folder (Save or open projects for future use). [+] ResH folder (includes ResHacker.exe). [+] UPX folder (includes upx32.exe and upx64.exe). [+] ATPL.EXE (AT4RE Power Loader). [+] Version History.txt1 point
-
1 point
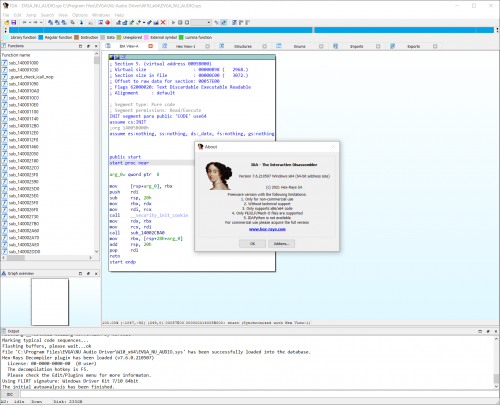 This (completely!) free version of IDA offers a privilege opportunity to see IDA in action. This light but powerful tool can quickly analyze the binary code samples and users can save and look closer at the analysis results. What’s included in the pack? Analyze both 32-bit and 64-bit applications Cloud-based x64 decompiler Local x86/x64 debugger included Support x86/x64 processors Save your analysis results Perpetual license The freeware version of IDA v7.6 comes with the following limitations: no commercial use is allowed lacks all features introduced in IDA > v7.6 cloud-based decompiler lacks certain advanced commands lacks support for many processors, file formats, etc… comes without technical support1 point
-
 1 point
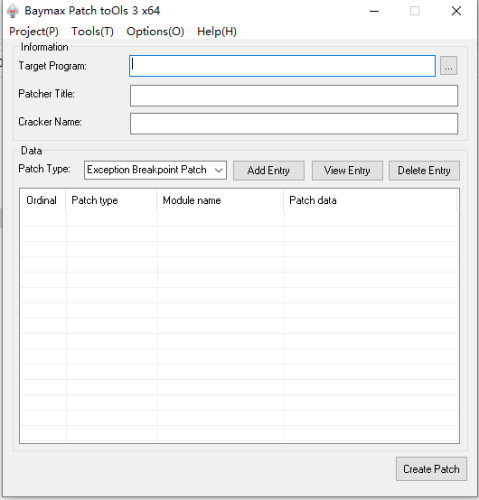 Baymax Patch Tools v3.1.0 Tool description: Baymax Patch Tools is a hijacking patch making tool that releases a hijacking DLL for the target process to load the function module PYG. Two patching functions are supported.search and replace patch supports feature code search and replace memory data, exception breakpoint patch supports simulating the exception breakpoint function of debugger and modifying register, memory and other data after setting and triggering breakpoint to achieve the purpose of modifying program execution flow and so on. The tool is protected, antivirus may misreport the tool and patch files! Due to the use of the shell SDK, all components of the tool (including the generated patches) do not contain networking capabilities! The generated patches will not modify any files on the system when running (except for overwriting patch files). The generated patches will not modify any files on the system when running (except for overwriting patch files). The tool itself has a verification mechanism and will load only after the module is successfully verified at startup, but for security reasons, please be sure to download and use it from the official site. Function introduction: . support hijacking crack, not modify the file itself . support for patching processes with dynamic base addresses (ASLR) . support patching multiple DLL modules of the target process . support patching different EXEs of the same patch . support patching the memory data of a process at a specified address . support for patching processes using feature code matching . support setting API HOOK decoding for shelled programs before patching data . support patching data after setting hardware breakpoint interrupt for the process . support setting exception breakpoints to modify the memory pointed to by registers or registers after interrupting the process . support setting conditional breakpoints for processes to determine whether to execute Patch according to the number of interrupts, . . . . register or memory values . support setting different conditional breakpoints for the same address to perform Patch on the interrupts that meet the conditions . support extracting global variables from assembly instructions to store and modify them . support for storing data and using stored data during process execution . support patching the memory pointed to by the memory marker after interrupt . support basic operations on data after interrupt . support for reading patch data from ini file . support to create memory keymaker . support for creating debug patches to troubleshoot patch problems by yourself Update: 2023.01.18 x86 v3.1.0 1. Support multi-language function 2. adjusted and optimized the UI, text descriptions, etc. to improve the interactive experience Download: https://sourceforge.net/projects/baymax-patch-tools/1 point
-
1 pointCode-caving is the practice of injecting machine code into a remote process and making it execute. In this tutorial, I will cover a method of code-caving which I like to call thread injection. Thread injection is a seven step process.1 point
-
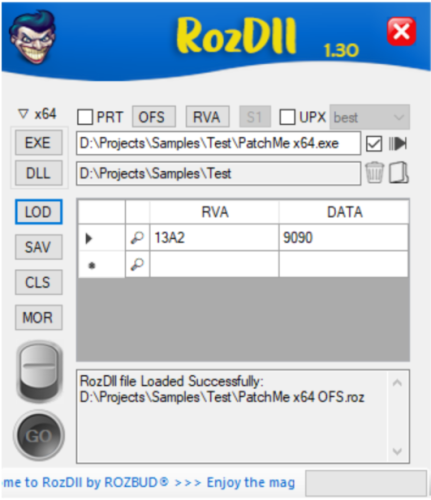 Provision: Create a tiny Proxy DLLs for Personal researches. RozDll Vs Fixit: Fixit is a “Static Load Generator”. Handles Pre-Generated List of DLL's that may be work with your Executable or not (same as ByMax). RozDll is a “Dynamic Load Generator”, runs your Executable in Memory, gets a list of Proxy DLL's which your Executable uses in Memory. RozDll Main Features: Generate Fast, Portable & Small Size Proxy/Hijacked DLL. Integrated with x64dbg. You can load the Patched Data directly from x64dbg exported file (*.1337). Dynamic Loading. Function Selection. Deferent Method of patch Options. Encryption: DLL Function Names are Encrypted. This will make it difficult for Anti-Virus to trace generated DLL. Startup Message: You can personalize your work by writing your name and short info/about. This message will appear only at the first run of target executable. Data Extraction: Upload Registry and other filetypes into target PC. Data Verification: Clicking on the 'Magnifier symbol' is mandatory & it will ensure that you entered the correct data. Created on Windows 10 & Visual Studio 2022. It should work on Windows 10 & Windows 11, but not guaranteed to work in Virtual Windows. Tutorial: RozDll_Advanced.mp4 RozDll_Final_Tutorial_(v1.30).mp41 point
-
 1 point
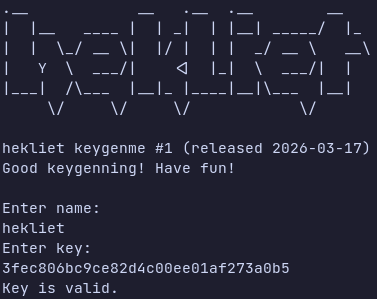 Not much to say there. Valid solution is a keygen that produces a valid key for any given name. Binaries for Linux and Windows are provided. Plain C, no symbols stripped, compiled with -O0, so should be fairly easy to follow. Difficulty is medium. Or perhaps easy for someone with some math knowledge. Here are some valid keys: Name: hekliet Key: 3fec806bc9ce82d4c00ee01af273a0b5 Name: Tuts 4 You Key: 40105e5bb69056bd3fdc1a4496fa9430 Name: Guybrush Threepwood Key: 400e09a63ee6d3a2bfd94d31f7369d101 point
-
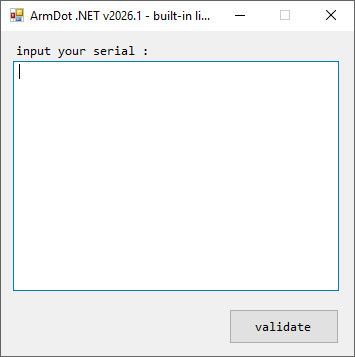 This one uses the built-in license system of the ArmDot .NET.. Provide a serial or an unpacked or a patched variant that accepts a serial.1 point
-
1 point
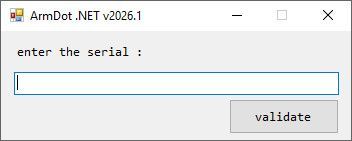 File protected with Hide strings Obfuscate control flow Obfuscate names Obfuscate namespaces and some virtualization accepted solution - unpack OR tell what is doing.1 point
-
 1 pointunDUP2 unpacker v0.3 | python to C++ port by Stingered (2026) Usage: Extract and dump the .dup2 and payload DLL to disk from a generated PE created by dUP 2. The .dup2 file can be loaded into diabl2oo2's Universal Patcher tool for editing. Sample output: ndup2 MyPatcher.exe unDUP2 unpacker v0.3 | python to C++ port by Stingered (2026) original python code: https://github.com/BakasuraRCE/UNdUP2 Usage: unDUP2.exe <file name> [+] Generated: MyPatcher.dumped.dll [+] Generated: MyPatcher.dUP2 (2 modules) *original python code: https://github.com/BakasuraRCE/UNdUP2 Note: As of now, this only works on Patchers, not Loaders generated by DUP2.1 point
-
 1 point
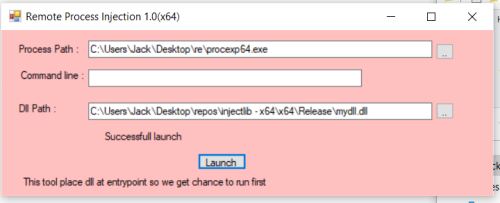 Remote Process Injection allow load dll to target entry point process . process remote injection 1.0.zip1 point
-
1 point
-

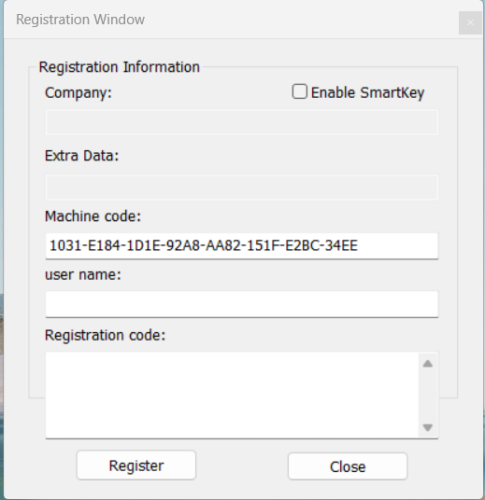 This is a WinLicense 3.2.2/sample, set by default, without adding an SDK in the source code, only adding a window function through an external plugin. I don't know if bypass can be cracked, I tested it and it doesn't. Shedding may be more complicated.Please use your own way to crack it. Whether it's molting, bypass, or keygen, they are all the best methods. No need to upload your proposal, posting a picture is the best answer. I will strive to learn towards your achievements. HWID:1031-E184-1D1E-92A8-AA82-151F-E2BC-34EE NAME:Mr.Leng .RegistCode:2FGP7NTY-22AMY4QL-XXEHAOKD-ZJKHKDKR-VY66SHXY-YTEQXVBF-GAXAEFIA-7BQWOTA5-5CE344K4-VBGMG25R-5TGP26WS-AIKQB3S5-5LDUHEHX-S6KSKH3H-OPPHIFAX-N6WPWIAM WinLicense3.2.2_sample.rar1 point
-
Today I release an unpacker script for Enigma Protector. Maybe you know that I created another unpacker script for Enigma in the past which no-longer works for protected Enigma files greater than 3.70+ and this is the reason why I wrote a new script, Enigma Alternativ Unpacker 1.0. So what is new in this script? This script will unpack your Enigma protected files and dump the used outer virtual machine. This means you do not need to use the DV / Enigma plugin which is used in my other script. Of course the virtual machine will be still virtualized but your unpacked files will work. It is not the best solution but for the moment it is a good "alternativ" and a working solution. Features of the script: ( 1.) Unpacking of ENIGMA 1.90 - 3.130+ ( 2.) RegSheme Bypass & HWID Changer ( 3.) Enigma CheckUp Killer ( 4.) VirtualMemory Dumper 1.90 - 3.x+ & SC Fixer M1 ( 5.) UIF Tool Necessary Sometimes! ( 6.) Enigma Intern Export & VM Scan + Log ( 7.) Improved Import Emulation Fixer ( 8.) Supports Exe & Dll Files [dll at EP!] This new script again covers almost all the protection features of Enigma Protector like my other script but it has been improved and I have added some extra things that you will see when you get to use it. I have created four video tutorials for you where you can see what you have to do in some of the different situations you may experience. Be sure that you "watch the videos" before you use the script to prevent some unnecessary questions where you can already find the answers if you watch them and then read my added text files. I also made an UnpackMe set with six different protected files (watch videos how to unpack all of them). If something does not work for you or if you get any trouble or have any questions then just post a reply on the topic (linked above) to get an answer.1 point
-
 1 pointREPT KeyGen Maker is an utility to make keygens easily without having a programming knowledges. Please report any bug/improve to make it better This is currently done in .NET so will need .NET Framework 3.5 or higher. Thanks for download it!1 point
-

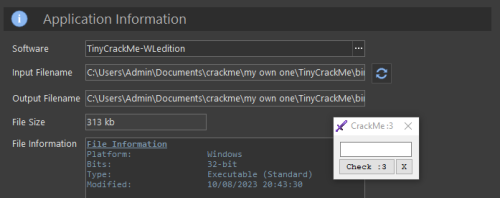 === SPOILER INSIDE SOURCE CODE TAB === A WinLicense'd version of TinyCrackMe Rules: 1. Unpack first 2. Do whatever you want after unpack, as long as ":3" MessageBox appear :3 Just want to see how long ppl will crack the latest version of WinLicense... WL Protection: - Anti-Debugger - Advanced API-Warping - Compress And Encrypt (all 3 options) - Full Encrypt Strings - Detect File/Registry Monitor - Entry Point Virt - Anti File Patching - Perform Protection Check - VMware/Virtual PC Allowed WLVM: - SHARK32 (Black, Red) - PUMA32 (Black, Red) - EAGLE32 (Black) Happy reversing :31 point
-
 1 point
-
 License User Details User Name=2days Tuts4you Company=The Terminator Hardware ID=6FF7-E7EF-5988-20FE-144E-865D-2D30-A73B Custom Data=<custom_start>Skynet, a global network of artificial intelligence machines.<custom_end> License Restrictions Days Expiration=365 Date Expiration=2029/12/12 Executions=999 Runtime execution=999 Global Time=999 Install Before Date=2029/01/01 Miscellaneous Unicode License=yes Generated License (FILE KEY) License Format=Binary License Data= <license_start> ghO1ud4wf14YNU87wUptZ1JTofTFErVAD+IwWKEjB/fxOtba9Vt0uasw45jdF3Yr9eGcJ/6h6lfad3d/MMYzxXYP7OZVGfHctljzMWS4H13UVl3DWBgWzCeozgy9k1UlULrL3/oKL/VdiS/BOJC98IgsF5+XT80xyGxos+Hcs4YdRarI9t0tj/+asJhpgN2KAXvH6lfp8qp0uvwZQUcnw/u+SpQjssOF5aAP9Bwweuw+6nfGxrZGcy8aNK3Kqo7rI5rLPk9Mzo1U0WkS1/I8lpQS1Mtticm1Am/eZCiCHJDMXDEfgTEuLGhQ9AItQtLQ2Fn8egx786AbJM09OEdiz5aGhz3kZfJZz8djMG3g8222gCmmDty8G4pBttMefKkVjKHoI2UXboNHpoOpxi53F6jldAhh3t+JoaOwa3Ng51uTfoNc2kLlCCP+jrjchZUNN9MY8y3kQ4K0Hd6eNkPAXwqbl2kakLZOlsmkkkVi9Pg620SzOt6YHh9iV1rS+TZ0jzWMvC9IakEgJionxYShgLg1Qkv6o4qIzP2ri9lMpM5eJK9Zo+Yl6K9HLnJ/gOE97Op7iAlywjsol5sunCIROe4pLHZo0PDNFJNZ4yy1VEgHp2+Qy/0nP55Fc8845MkE4hrjpg7SOFphFILgTuGVPG97nhRDTi05+f50WE2rl5PpuXnmeBblgD7S87p2tHUO7o2t8kvI/z7Xd9xNfw4HYJcbztKPxAkamUdIl0jmnhdIRGJMlYZm7rBgLd6dYhEu6Lo8P5vi7tydId4QsuwC7tv6+F8CQ1n6HpXSoPowKuMI/L2Zg1Ry3jlS2KUvH4spGy3URvJ8e2rFaDZpmQ== <license_end> File Information Platform: Windows Bits: 64-bit Type: Executable (Standard) Version: 1.0.0.2 Modified: 8/1/2023 12:09:04 PM Protection Macros Virtual Machine: 10 Mutate: 0 String Encrypt: 6 CheckProtection: 2 CheckCodeIntegrity: 0 CheckVirtualPC: 1 CheckDebugger: 1 Unprotected: 0 CheckRegistration: 0 Registered: 0 Unregistered: 0 WinLicense x64 (version 3.1.3.0) Unit_bypassme.pas1 point
-
 1 point
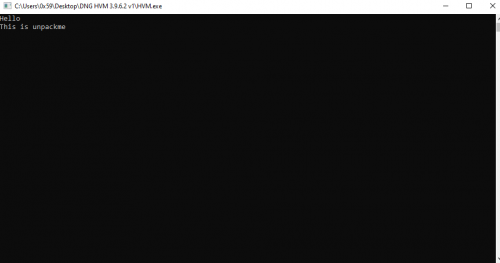 This file is protected using DNGuard HVM 3.9.6.2 Protections used : HVM Jit Challenge is to unpack and post details of methods used.1 point
-
 1 point
 A simple console application that displays the HWID and asks you to enter an "activation key" for it. Key format: xxxxxxxx-xxxxxxxx-xxxxxxxx-xxxxxxxx-xxxxxxxx-xxxxxxxx-xxxxxxxx-xxxxxxxx-xxxxxxxx-xxxxxxxx The solution will be a description of the algorithm to generate an activation key for any HWID value (there is no need to write code). P. S. Archive password: 1231 point
-
 1 point
-
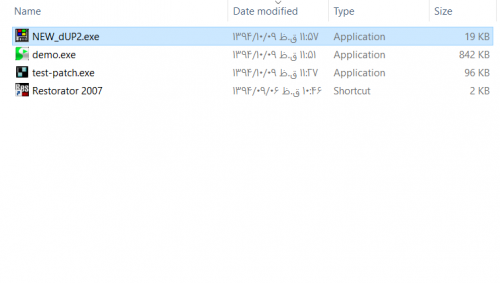 NEW dUP2 - Friendly with antivirus Password: tuts4you.com1 point
-
PACE/Ilok is mostly loved by the audio industry, and since we crackers don't care too much about hardcore audio apps PACE is not well documented. But this protection is actually quite decent and fun to reverse, it is not especially hard but enough to stop most mediocre crackers. However one aspect could be especially hard for the less determined. That is the driver TPkd.sys, it has some nice features that can stop you dead in your tracks. In this paper I will discuss in my opinion the best aspect of this driver, resolving the int3 stolen calls.1 point
-
1 point
-
1 point
 Lighthouse is a powerful code coverage plugin for IDA Pro and Binary Ninja. As an extension of the leading disassemblers, this plugin enables one to interactively explore code coverage data in new and innovative ways when symbols or source may not be available for a given binary. This plugin is labeled only as a prototype & code resource for the community.1 point
-
1 point
 MicroAVX is an extension of the IDA Pro decompiler, adding partial support for a number of common instructions from Intel's Advanced Vector Extensions (AVX). This plugin demonstrates how the Hex-Rays microcode can be used to lift and decompile new or previously unsupported instructions. There are no plans further develop MicroAVX, or extend its coverage to the complete set of AVX instructions. This plugin is labeled only as a prototype & code resource for the community.1 point
-
1 point
 Prefix is a small function prefixing plugin for IDA Pro. The plugin augments IDA's function renaming capabilities by adding a handful of convenient prefixing actions to relevant right click menus.1 point
-
1 point
 Lucid is a developer-oriented IDA Pro plugin for exploring the Hex-Rays microcode. It was designed to provide a seamless, interactive experience for studying microcode transformations in the decompiler pipeline. This plugin is labeled only as a prototype & code resource for the community. Please note that it is a development aid, not a general purpose reverse engineering tool.1 point
-
1 point
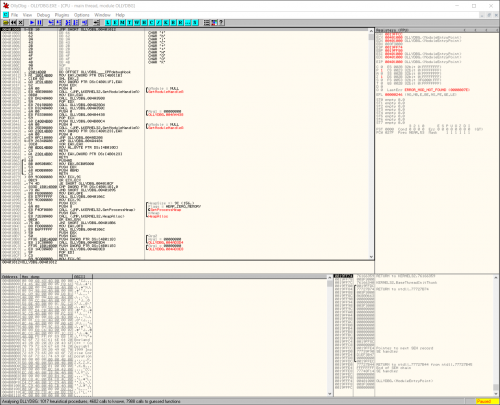 OllyDbg is a 32-bit assembler level analysing debugger for Microsoft® Windows®. Emphasis on binary code analysis makes it particularly useful in cases where source is unavailable. OllyDbg is a shareware, but you can download and use it for free. Special highlights are: Intuitive user interface, no cryptical commands Code analysis - traces registers, recognizes procedures, loops, API calls, switches, tables, constants and strings Directly loads and debugs DLLs Object file scanning - locates routines from object files and libraries Allows for user-defined labels, comments and function descriptions Understands debugging information in Borland® format Saves patches between sessions, writes them back to executable file and updates fixups Open architecture - many third-party plugins are available No installation - no trash in registry or system directories Debugs multithread applications Attaches to running programs Configurable disassembler, supports both MASM and IDEAL formats MMX, 3DNow! and SSE data types and instructions, including Athlon extensions Full UNICODE support Dynamically recognizes ASCII and UNICODE strings - also in Delphi format! Recognizes complex code constructs, like call to jump to procedure Decodes calls to more than 1900 standard API and 400 C functions Gives context-sensitive help on API functions from external help file Sets conditional, logging, memory and hardware breakpoints Traces program execution, logs arguments of known functions Shows fixups Dynamically traces stack frames Searches for imprecise commands and masked binary sequences Searches whole allocated memory Finds references to constant or address range Examines and modifies memory, sets breakpoints and pauses program on-the-fly Assembles commands into the shortest binary form Starts from the floppy disk and much, much more!1 point
-
Sometimes crackme's or something you might be reversing will constantly bug you due to excessive usage of F7 & F8. It will be quite neat if you can see how the application is executing visually and set you breakpoints accordingly. I know stuff like offensivecomputing.net VERA exists but most of the time it crashes. Here is my attempt and I hope you find it useful.1 point
-
When new malware are discovered, it is important for researchers to analyze and understand them as quickly as possible. This task has been made more difficult in recent years as researchers have seen an increasing use of virtualization-obfuscated malware code. These programs are difficult to comprehend and reverse engineer, since they are resistant to both static and dynamic analysis tech-techniques. Current approaches to dealing with such code first reverse-engineer the byte code interpreter, then use this to work out the logic of the byte code program. This outside-in approach produces good results when the structure of the interpreter is known, but cannot be applied to all cases. This paper proposes a different approach to the problem that focuses on identifying instructions that affect the observable behaviour of the obfuscated code. This inside-out approach requires fewer assumptions, and aims to complement existing techniques by broadening the domain of obfuscated programs eligible for automated analysis. Results from a prototype tool on real-world malicious code are encouraging.1 point
-
A premier collection of articles compiled by Fly from the now defunct UnPack China forum dated in 2007. Note that most of the content contained in this compilation is in Chinese, you may need to use a translator to fully understand some of the information it contains.1 point
-
I wrote this little hook-engine for a much bigger article. Sometimes it seems such a waste to write valuable code for large articles whose topic isn't directly related to the code. This often leads to the problem that the code won't be found by the people who are looking for it. Personally, I would've used Microsoft's Detour hook engine, but the free license only applies to x86 applications, and that seemed a little bit too restrictive to me. So, I decided to write my own engine in order to support x64 as well. I've never downloaded Detour nor have I ever seen its APIs, but from the general overview given by Microsoft it's easy to guess how it works. As I said, this is only a part of something bigger. It's not perfect, but it can easily become such. Since this is not a beginner's guide about hooking, I assume that the reader already possesses the necessary knowledge to understand the material. If you never heard about this subject, you'd better start with another article. There's plenty of guides out there, no need to repeat the same things here. As everybody knows there's only one easy and secure way to hook a Win32 API: to put an inconditional jump at the beginning of the code to redirect it to the hooked function. And by secure I just mean that our hook can't be bypassed. Of course, there are some other ways, but they're either complicated or insane or both. A proxy dll, for instance, might work in some cases, but it's rather insane for system dlls. Overwriting the IAT is unsecure for two reasons: a) The program might use GetProcAddress to retrieve the address of an API (and in that case we should handle this API as well). b) It's not always possible, there are many cases as for packed programs where the IAT gets built by the protection code and not by the Windows loader. Ok, I guess you're convinced. Let's just say that there's a reason why Microsoft uses the method presented in this article.1 point
-
1 pointHooking is the practice of re-directing the flow of a program causing it to execute a code-cave or function in an injected module in place of another piece of code. In this tutorial, I will cover a method of hooking known as IAT (Import Address Table) Hooking. IAT Hooking is a 4 step process (I assume you are able to manage to inject the attacking DLL on your own).1 point
-
 1 pointOllyICE patched to work with TheMida, this was made by the prestigious team SnD member EvOlUtIoN. This debugger took me a long time to find on the net and since most of the links that were on the net were dead it took me like around 3 weeks to find. I hope you guys enjoy. QUOTE BY EvOlUtIoN: So, by popular demand here is the debugger I normally use to "play" with programs protected with TheMida / WinLicense. My patch is very simple but it is good to remember that OllyICE was created for the first time since Hachno, a guru when it comes to Armadillo and unpacking in general. This version has basically 2 patches that differ from the normal OllyICE: One. We do not crash when you load a file protected 2. If you add a context menu creates an entry called "TheMida OllyDbg", so depending on the target, you can open a olly or another. In the plugin folder there are all those necessary, the most important are: 1. PHANTOM plugin 2. HideOD Without these you do not ever riusicrà to load a target with TheMida without being detected. In addition there are 2 scripts, neither Dumpa the VM but at least find the OEP and aaggiustano the IAT.1 point