Leaderboard
-
CodeExplorer
Team Retired1,109Points4,868Posts -
lovejoy226
Full Member+226Points1,467Posts -
dawwinci
Full Member197Points105Posts -
whoknows
Full Member+156Points2,058Posts
Popular Content
Showing content with the highest reputation since 10/12/2025 in all areas
-
 10 pointsApologies for the downtime! There was a broken repo update rolled out over the weekend and hosting stated they were to fix it. In between then and now they said they sent me emails I haven't received, requesting information from me, and chat support repeatedly didn't update the support ticket with the information I provided. It has been a debacle. It did not help being a long weekend here and me being busy. In the end, when I was available, I had to tidy things up and get the last of the issues fixed up. If you experience any problems please let me know so that I can check it out, and get it resolved, thank you... Ted.10 points
-
6 pointsA collection of tutorials aimed particularly for newbie reverse engineers. 01. Olly + assembler + patching a basic reverseme 02. Keyfiling the reverseme + assembler 03. Basic nag removal + header problems 04. Basic + aesthetic patching 05. Comparing on changes in cond jumps, animate over/in, breakpoints 06. "The plain stupid patching method", searching for textstrings 07. Intermediate level patching, Kanal in PEiD 08. Debugging with W32Dasm, RVA, VA and offset, using LordPE as a hexeditor 09. Explaining the Visual Basic concept, introduction to SmartCheck and configuration 10. Continued reversing techniques in VB, use of decompilers and a basic anti-anti-trick 11. Intermediate patching using Olly's "pane window" 12. Guiding a program by multiple patching. 13. The use of API's in software, avoiding doublechecking tricks 14. More difficult schemes and an introduction to inline patching 15. How to study behaviour in the code, continued inlining using a pointer 16. Reversing using resources 17. Insights and practice in basic (self)keygenning 18. Diversion code, encryption/decryption, selfmodifying code and polymorphism 19. Debugger detected and anti-anti-techniques 20. Packers and protectors : an introduction 21. Imports rebuilding 22. API Redirection 23. Stolen bytes 24. Patching at runtime using loaders from lena151 original 25. Continued patching at runtime & unpacking armadillo standard protection 26. Machine specific loaders, unpacking & debugging armadillo 27. tElock + advanced patching 28. Bypassing & killing server checks 29. Killing & inlining a more difficult server check 30. SFX, Run Trace & more advanced string searching 31. Delphi in Olly & DeDe 32. Author tricks, HIEW & approaches in inline patching 33. The FPU, integrity checks & loader versus patcher 34. Reversing techniques in packed software & a S&R loader for ASProtect 35. Inlining inside polymorphic code 36. Keygenning 37. In-depth unpacking & anti-anti-debugging a combination packer / protector 38. Unpacking continued & debugger detection by DLL's and TLS 39. Inlining a blowfish scheme in a packed & CRC protected dll + unpacking Asprotect SKE 2.2 40. Obfuscation and algorithm hiding6 points
-
 5 points
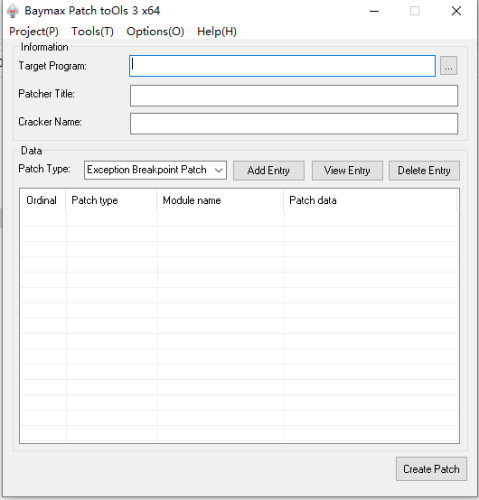 2025.10.15 — x86/x64 v3.5.1.3 1.Patch customization: added a batch of hijack DLLs and you can configure hijack modules on the "Custom Patch Settings" page. Patches can now bundle custom files — non-PE files will be extracted to the target directory together with the patch, while other files can be optionally extracted. Patch data in the cracking modules PYG/PYG64 now supports dynamic expansion. 2.Added a small utility: “Process Hijack DLL Detector” — provides a closed loop from detecting usable hijack DLLs → generating a hijack DLL project → adding that custom hijack module into a patch. 3.The hijack code generator is now compatible with the latest VS2022; fixed intermediate directory settings. 4.When the patch logo popup is closed, the target application's main window is brought to the foreground. 5.The main program now generates a dump file when it crashes. 6.Fixed compatibility issues with VMP 3.x and several bugs — thanks to csjwaman and 真小白 for their bug reports. 7.Added tooltip (tip bubble) support on UI controls so full text can be displayed. 8.Thanks to KuNgBiM and 红豆 for providing multilingual files and proofreading copy. 9.Improved data protection, compatibility, and anti-debugging; thanks to kxoe for the suggestions. 10.Minor UX/details optimizations in the main program — for example, improved prompts when saving bpt projects. Baymax Patch Tools v3.5.1.3.zip Baymax Patch Tools x64 v3.5.1.3.zip Baymax toOls for x64dbg v1.9.5 1. Add replacement function for search data 2. Add feature code option with real-time effect 3. Add more language files Baymax toOls for x64dbg v1.9.5.zip5 points
-
 4 points
-
 3 points
Latest release (3.5.1.7) with tuts/videos re-uploaded (English docs under release folders). I hope these will help (sorry, I cannot translate from Chinese 🥺) --> Download3 points
-
 3 points
 You dont know even how our forums works I think... Before write any thread you must READ RULES... Our forum based on when you write a good topic you earn 2 points with points you can download Attachements... If you write thank you...etc you do not earn any thing if you write same reply in multiple threads you get banned If you hate our forums leave bro it's very simple...3 points
-
3 points
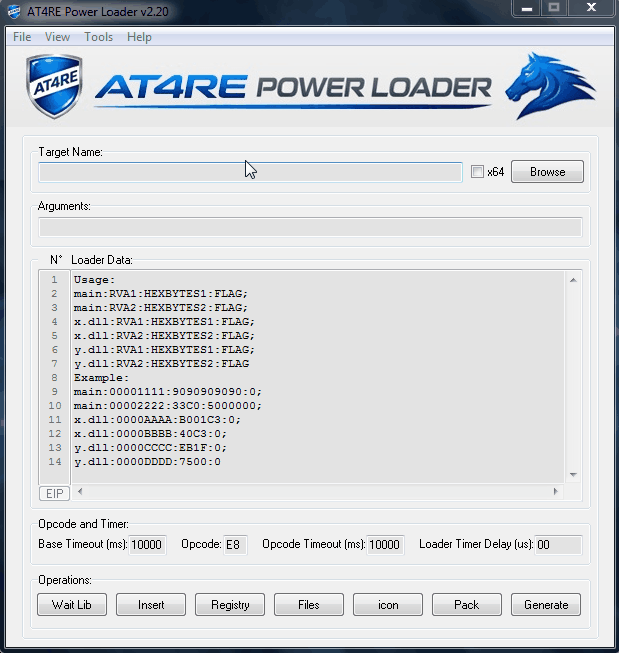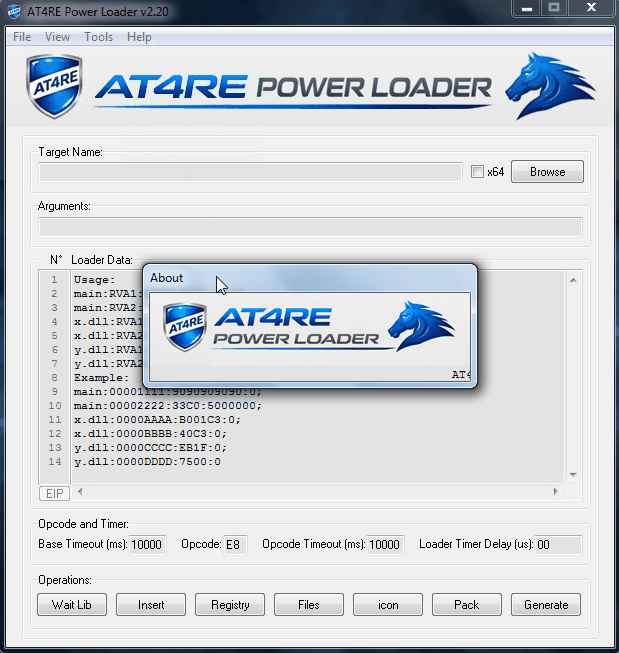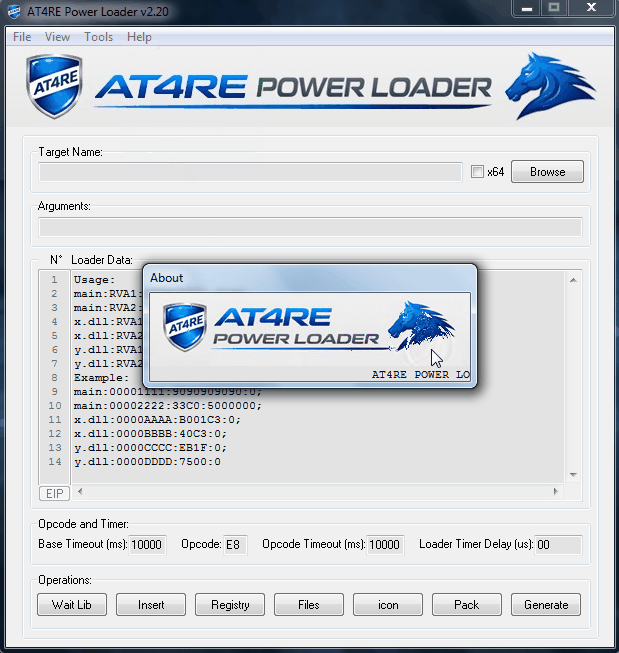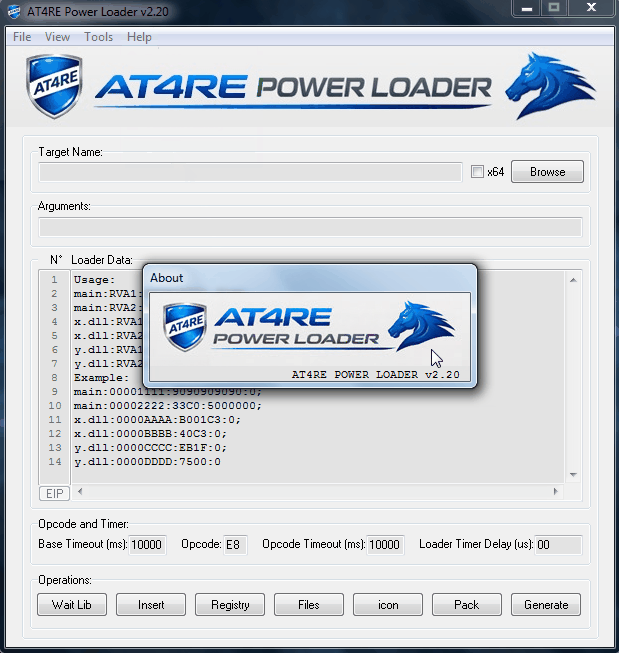
Some times to make patch to DLL file with our tool you need to understand when dll target get unpacked firstly this is the most important, and for that you need to understand the best moment of pointer position in main exe while debugging, our Loader able to detect Static Opcode in Static Stack, if you use this way you can Creat a Strong Loader for your Target EXE or DLL.3 points
-
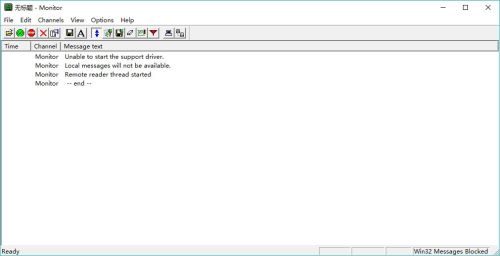 DriverMonitor Enhanced Edition (Alpha) Enhance - 1 - Support for file dragging operations has been implemented, allowing direct setting of the path for the corresponding driver file. - 2 - Drag-and-drop operation compatible with administrator mode has been implemented. - 3 - Folder directory redirection in 64-bit environment has been disabled. Modified by boot @ tuts4you Date July 6, 20262 points
-
 2 points
 IDA Palette (or its project name: ifred) is a plugin which provides fast search on IDA Pro's commands/menu items or searches through its strings output! This plugin provides 2 keyboard shortcuts: Ctrl + P : Searched through IDA's commands Ctrl + Shift +P : Searched through IDA's string output2 points
-
2 points
Firstly You Must Set Hardware Breakpoints on your Target address (where you want to make changes) Then You Must Break on System DLL Entry (For Identify the last Loaded DLL Before The Pointer Stop on your Target address) Finally Set Memory Breakpoint on Write at .data Section of your main EXE Here we Go Like Last Example: Our DLL Befor Stop at our address is: wsock32.dll Next Step Restart Target and Finding Static Opcode in Static Stack and check our DLL Target Code if Unpacked Summary: main:0002064F:10:0; tgsdk.dll:00006310:00:0; tgsdk.dll:00006638:74:0When Our Loader Loop Checking First Byte of RVA 1 in Stack and when Checking is OK, That means EIP is running in 004012EC, and our Target DLL is unpacked and ready to write the Loader Data. I hope This Tuto Can Help Greetings AT4RE2 points
-
The Hex-Rays Decompiler plugin for better code navigation in RE process. CodeXplorer automates code REconstruction of C++ applications or modern malware like Stuxnet, Flame, Equation, Animal Farm ... Features: Automatic type REconstruction for C++ objects. To be able to reconstruct a type using HexRaysCodeXplorer one needs to select the variable holding pointer to the instance of position independed code or to an object and by right-button mouse click select from the context menu «REconstruct Type» option. Virtual function table identification - automatically identifies references to virtual function tables during type reconstruction. When a reference to a virtual function table is identified the plugin generates a corresponding C-structure. As shown below during reconstructing struct_local_data_storage two virtual function tables were identified and, as a result, two corresponding structures were generated: struct_local_data_storage_VTABLE_0 and struct_local_data_storage_VTABLE_4. C-tree graph visualization – a special tree-like structure representing a decompiled routine in citem_t terms (hexrays.hpp). Useful feature for understanding how the decompiler works. The highlighted graph node corresponds to the current cursor position in the HexRays Pseudocode window Ctree Item View – show ctree representation for highlighted element Extract Types to File – dump all types information (include reconstructed types) into file. Navigation through virtual function calls in HexRays Pseudocode window. After representing C++ objects by C-structures this feature make possible navigation by mouse clicking to the virtual function calls as structure fields Jump to Disasm - small feature for navigate to assembly code into "IDA View window" from current Pseudocode line position. It is help to find a place in assembly code associated with decompiled line. Object Explorer – useful interface for navigation through virtual tables (VTBL) structures. Object Explorer outputs VTBL information into IDA custom view window. The output window is shown by choosing «Object Explorer» option in right-button mouse click context menu Support auto parsing RTTI objects This plugin is recompiled by disauto UPDATE 29.10.2024 Recompiled for IDA Pro v9.0 Windows x86_642 points