Leaderboard
-
cyberbob
Full Member9Points82Posts -
ivankozlovsky
Junior9Points3Posts -
Progman
Full Member7Points515Posts -

Rouse_
Junior5Points1Posts
Popular Content
Showing content with the highest reputation since 10/15/2026 in all areas
-
 Yes, server is patched... Ted.3 points
-
 The number 4, 🤣 The Private Key for a Globally Trusted Certificate Authority Was the Number 4 eMudhra Intermediate CA Compromise: The Trust Stores You Patched, and the Ones You Didn't Know You Had eMudhra Intermediate CA Compromise PowerShell script downloads a cryptographically verified list of compromised or impacted intermediate certificates from a remote manifest and automatically moves them into the Windows Disallowed (Untrusted Certificates) certificate store to block them system-wide. Step-by-step: Administrative & Version Safeguards (#Requires) Enforces PowerShell version 5.1 or newer and requires the script to be run with Administrator privileges (-RunAsAdministrator). If not run as admin, it halts immediately. $ErrorActionPreference = 'Stop' ensures that any minor error or failed command stops the script entirely rather than continuing silently. Temporary File Setup (GetTempFileName) Creates a secure, randomized temporary file on disk ($file) to safely store the downloaded JSON manifest and process the certificate binaries. Secure Download and Hash Verification (Invoke-WebRequest & Get-FileHash) Downloads the remote JSON manifest from [https://emudhra.we-have-a-problem.com/impacted-intermediates.json](https://emudhra.we-have-a-problem.com/impacted-intermediates.json). Calculates the SHA-256 hash of the downloaded file and compares it against a hardcoded security hash (F67B3ABE9B4...). If the file has been tampered with or modified in transit, it throws an error and aborts immediately, preventing untrusted payloads from running. Decoding and Importing into the Disallowed Store (Import-Certificate) Parses the JSON content to read the individual certificate entries. For each certificate, it strips out the PEM boundary headers and whitespace, converts the raw Base-64 text back into binary bytes, and writes them back into the temporary file. Imports each certificate into Cert:\LocalMachine\Disallowed. Moving a certificate to the Disallowed store forces Windows to explicitly untrust and block any connection or file signed by it. Cleanup (finally Block) The finally block guarantees that whether the script succeeds or throws an error, the temporary file created on disk is securely deleted (Remove-Item), leaving no residual files behind. #Requires -Version 5.1 #Requires -RunAsAdministrator $ErrorActionPreference = 'Stop' Import-Module PKI $file = [IO.Path]::GetTempFileName() try { Invoke-WebRequest -UseBasicParsing -Uri 'https://emudhra.we-have-a-problem.com/impacted-intermediates.json' -OutFile $file if ((Get-FileHash -LiteralPath $file -Algorithm SHA256).Hash -ne 'F67B3ABE9B4879F4E91874ED041BECCD71257F1DB41C588C724CCF12AA90C59E') { throw 'Manifest SHA-256 mismatch. No certificates were imported. Review the advisory before updating the pinned hash.' } $certificates = Get-Content -LiteralPath $file -Raw -Encoding UTF8 | ConvertFrom-Json foreach ($certificate in $certificates) { $base64 = $certificate.pem -replace '-----BEGIN CERTIFICATE-----|-----END CERTIFICATE-----|\s', '' [IO.File]::WriteAllBytes($file, [Convert]::FromBase64String($base64)) Import-Certificate -FilePath $file -CertStoreLocation Cert:\LocalMachine\Disallowed } } finally { Remove-Item -LiteralPath $file }2 points
-
Invision Community is running on PHP it seems. @Teddy Rogers are we safe and patched?2 points
-
 AI tools discovered the PHP vulnerability that could take down 70% of the internet. Critical vulnerabilities in the PHP web scripting language could allow hackers to take control of any website running the widely used software, PHP’s developers said on Wednesday, as they released emergency updates that sent website owners scrambling to fix the flaws.1 point
-
Update. This took a while, but I was able to generate a signing cert (.pfx file) for PE files. Won't do kernel drivers, of course, but worth the effort IMO.1 point
-
Best meme even if not accurate.1 point
-
I want to release a new tutorial about the popular theme Themida - WinLicense. So I see there seems to be still some open questions mostly if my older unpack script does not work anymore and the unpacked files to, etc. So this time I decided to create a little video series on how to unpack and deal with a newer protected Themida target manually where my older public script does fail. A friend of mine did protect unpackme's for this and in the tutorial you will see all steps from A-Z to get this unpackme successfully manually unpacked but this is only one example how you can do it, of course. So the tutorial [videos + text tutorial] is very long and has a run-time of more than three hours and of course it will be necessary that you also read the text parts I made at the same time if possible but if you are already a advanced user then you will have it easier than a newbie. So I hope that you have enough patience to work through the whole tutorial. So the main attention I set on all things which happen after normal unpacking so the unpack process is the simplest part and all what comes after is the most interesting part and how to deal with all problems that happen. It's more or less like a live unpack session. I also wrote some small basic little helper scripts which you can also use for other targets to get valuable information if you need. Short summation: Unpacking Exception analysing VM analysing with UV plugin AntiDump's find & fixing & redirecting "after fix method" Testing on other OS My Special Thanks goes to Lostin who made this unpackme and others + OS's tests. (I want to send a thank you to Deathway again for creating this very handy and helpfully UV plugin). So this is all I have to say about the tutorial so far, just watch and read and then try it by yourself. Oh! and by the way I record ten videos and not only one. If something does not work or you have any problems with this tutorial, etc. then ask in the support topic only. Don't send me tons of PM's, OK! Thank you in advance. PS: Oh! and before someone has again something to complain because of my tutorial style [goes to quickly or is bad or whatever] then I just want to say, maybe you're right so normally I don't like to create and write tutorials. This is really not my thing so keep this in your mind.1 point
-
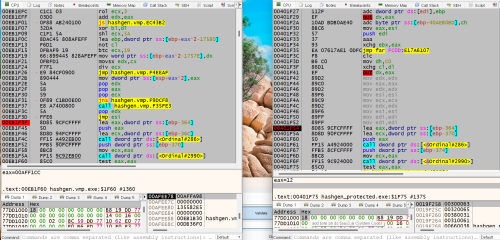 I want you guys who are capable of unvirtualizing and unpacking them to upload the final ones. These files are just the same part of the codes virtualized which are 2 lines of the original mfc source codes. So if you can unvirtualize them and unpack them, please upload the final ones. Any other protections are excluded absolutely. Give it a try and improve your skills. Best Regards. sean.1 point
-
1 point
-

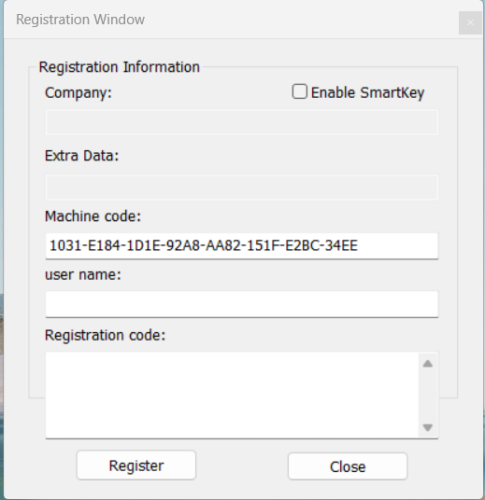 This is a WinLicense 3.2.2/sample, set by default, without adding an SDK in the source code, only adding a window function through an external plugin. I don't know if bypass can be cracked, I tested it and it doesn't. Shedding may be more complicated.Please use your own way to crack it. Whether it's molting, bypass, or keygen, they are all the best methods. No need to upload your proposal, posting a picture is the best answer. I will strive to learn towards your achievements. HWID:1031-E184-1D1E-92A8-AA82-151F-E2BC-34EE NAME:Mr.Leng .RegistCode:2FGP7NTY-22AMY4QL-XXEHAOKD-ZJKHKDKR-VY66SHXY-YTEQXVBF-GAXAEFIA-7BQWOTA5-5CE344K4-VBGMG25R-5TGP26WS-AIKQB3S5-5LDUHEHX-S6KSKH3H-OPPHIFAX-N6WPWIAM WinLicense3.2.2_sample.rar1 point
-

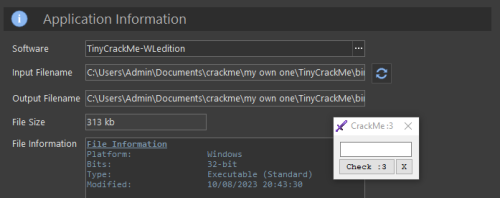 === SPOILER INSIDE SOURCE CODE TAB === A WinLicense'd version of TinyCrackMe Rules: 1. Unpack first 2. Do whatever you want after unpack, as long as ":3" MessageBox appear :3 Just want to see how long ppl will crack the latest version of WinLicense... WL Protection: - Anti-Debugger - Advanced API-Warping - Compress And Encrypt (all 3 options) - Full Encrypt Strings - Detect File/Registry Monitor - Entry Point Virt - Anti File Patching - Perform Protection Check - VMware/Virtual PC Allowed WLVM: - SHARK32 (Black, Red) - PUMA32 (Black, Red) - EAGLE32 (Black) Happy reversing :31 point
-
 License User Details User Name=2days Tuts4you Company=The Terminator Hardware ID=6FF7-E7EF-5988-20FE-144E-865D-2D30-A73B Custom Data=<custom_start>Skynet, a global network of artificial intelligence machines.<custom_end> License Restrictions Days Expiration=365 Date Expiration=2029/12/12 Executions=999 Runtime execution=999 Global Time=999 Install Before Date=2029/01/01 Miscellaneous Unicode License=yes Generated License (FILE KEY) License Format=Binary License Data= <license_start> ghO1ud4wf14YNU87wUptZ1JTofTFErVAD+IwWKEjB/fxOtba9Vt0uasw45jdF3Yr9eGcJ/6h6lfad3d/MMYzxXYP7OZVGfHctljzMWS4H13UVl3DWBgWzCeozgy9k1UlULrL3/oKL/VdiS/BOJC98IgsF5+XT80xyGxos+Hcs4YdRarI9t0tj/+asJhpgN2KAXvH6lfp8qp0uvwZQUcnw/u+SpQjssOF5aAP9Bwweuw+6nfGxrZGcy8aNK3Kqo7rI5rLPk9Mzo1U0WkS1/I8lpQS1Mtticm1Am/eZCiCHJDMXDEfgTEuLGhQ9AItQtLQ2Fn8egx786AbJM09OEdiz5aGhz3kZfJZz8djMG3g8222gCmmDty8G4pBttMefKkVjKHoI2UXboNHpoOpxi53F6jldAhh3t+JoaOwa3Ng51uTfoNc2kLlCCP+jrjchZUNN9MY8y3kQ4K0Hd6eNkPAXwqbl2kakLZOlsmkkkVi9Pg620SzOt6YHh9iV1rS+TZ0jzWMvC9IakEgJionxYShgLg1Qkv6o4qIzP2ri9lMpM5eJK9Zo+Yl6K9HLnJ/gOE97Op7iAlywjsol5sunCIROe4pLHZo0PDNFJNZ4yy1VEgHp2+Qy/0nP55Fc8845MkE4hrjpg7SOFphFILgTuGVPG97nhRDTi05+f50WE2rl5PpuXnmeBblgD7S87p2tHUO7o2t8kvI/z7Xd9xNfw4HYJcbztKPxAkamUdIl0jmnhdIRGJMlYZm7rBgLd6dYhEu6Lo8P5vi7tydId4QsuwC7tv6+F8CQ1n6HpXSoPowKuMI/L2Zg1Ry3jlS2KUvH4spGy3URvJ8e2rFaDZpmQ== <license_end> File Information Platform: Windows Bits: 64-bit Type: Executable (Standard) Version: 1.0.0.2 Modified: 8/1/2023 12:09:04 PM Protection Macros Virtual Machine: 10 Mutate: 0 String Encrypt: 6 CheckProtection: 2 CheckCodeIntegrity: 0 CheckVirtualPC: 1 CheckDebugger: 1 Unprotected: 0 CheckRegistration: 0 Registered: 0 Unregistered: 0 WinLicense x64 (version 3.1.3.0) Unit_bypassme.pas1 point
-
 1 point
 A simple console application that displays the HWID and asks you to enter an "activation key" for it. Key format: xxxxxxxx-xxxxxxxx-xxxxxxxx-xxxxxxxx-xxxxxxxx-xxxxxxxx-xxxxxxxx-xxxxxxxx-xxxxxxxx-xxxxxxxx The solution will be a description of the algorithm to generate an activation key for any HWID value (there is no need to write code). P. S. Archive password: 1231 point
-
 1 point